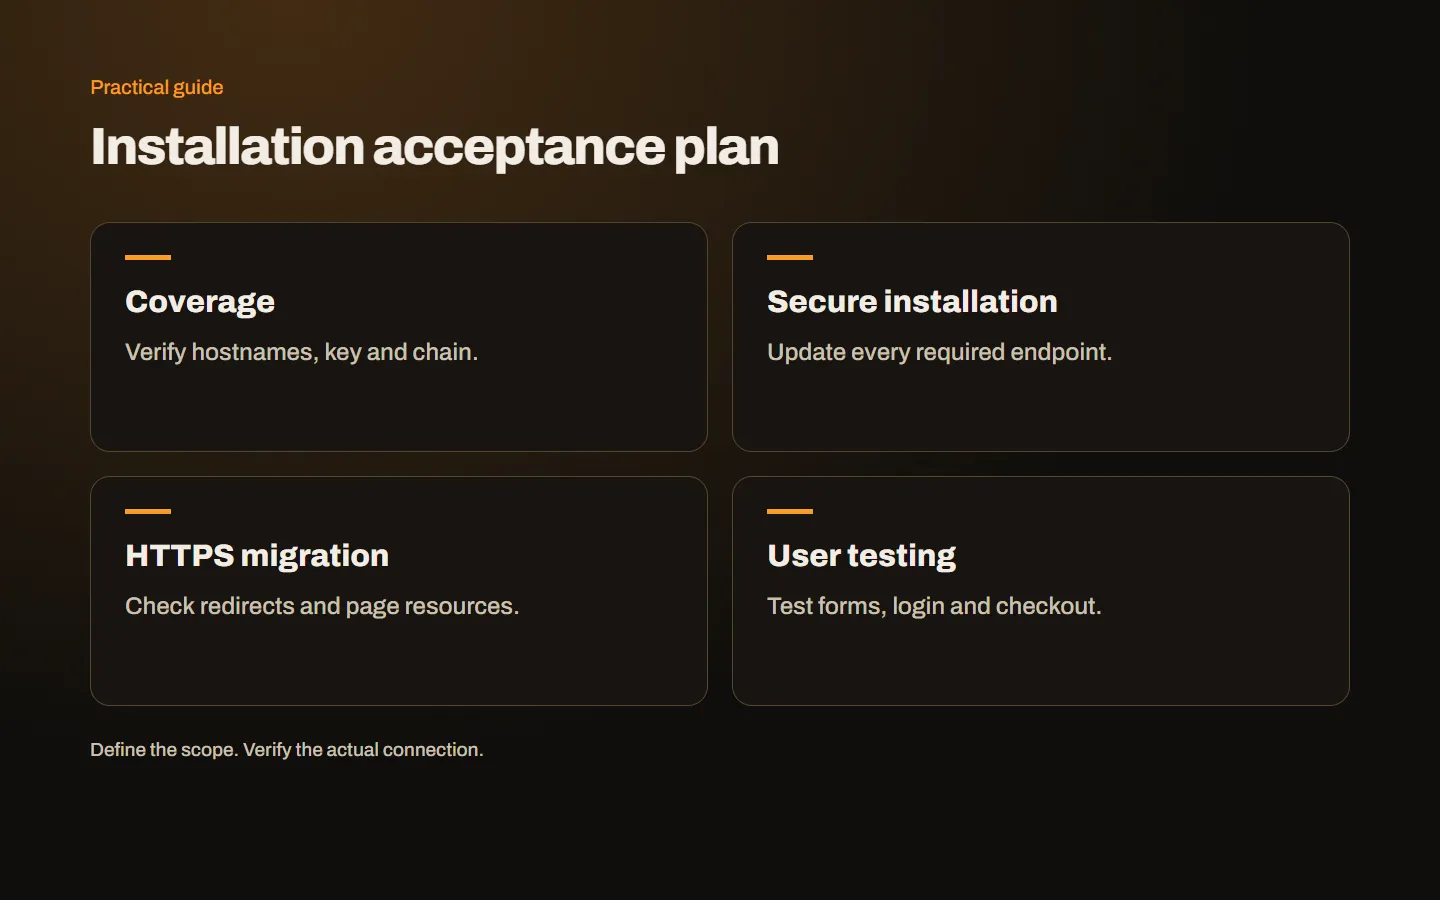
Issuance is not the same as a finished HTTPS installation. A certificate on the wrong endpoint, an incomplete chain or an old HTTP resource can still cause visible failures. This checklist follows the work from preparation through visitor testing and maintenance handover, with a concrete result expected at each stage.
Record the current services
List the apex domain, www and every relevant subdomain. Identify the server, CDN or managed platform behind each one. Keep mail, API and web services separate when they have different endpoints. One parent domain does not imply one TLS termination point, and a control panel entry does not prove that every service has been updated.
Back up the working configuration securely and assign a rollback owner. Decide which services could be affected and choose a suitable change window. Avoid combining the certificate work with unrelated redesign or URL changes when possible. A focused change is easier to investigate if a critical customer action stops working during deployment.
Match the issued names
Inspect the certificate’s alternative names against the inventory. example.com and www.example.com are distinct. *.example.com can cover panel.example.com but not api.eu.example.com, and the apex requires separate inclusion. Check the actual issued certificate as well as the order details so that a transcription error is caught before acceptance.
An HTTPS alias used only for redirection still needs valid initial coverage. The browser performs TLS checks before receiving the redirect response. Correct the name coverage rather than assuming the redirect makes the warning irrelevant. Our Wildcard guide and selection guide explain how to build a scope that matches the real entry addresses.
Protect and match the private key
The private key is different from the certificate and certificate signing request. The installation team should verify that the issued certificate corresponds to the intended key. If a platform manages this internally, avoid exporting unnecessary copies. The purpose is correct deployment and controlled access, not producing more files than the service actually needs.
Keep private keys out of public web directories, broadly shared folders and ordinary support messages. Review access when teams change. If a key may have been exposed, renaming its file is not a remedy. Plan replacement keys, reissuance and appropriate revocation steps. These actions should be coordinated across every endpoint that used the affected key.
Serve the proper chain
Browsers need an appropriate trust chain, not merely the site’s leaf certificate. Missing or incorrect intermediates can lead to different results across devices. One successful browser test is not enough to prove that the chain is correctly served for all relevant clients. Follow the authority’s current installation instructions for the target server.
Do not reuse an intermediate bundle from an old order without checking suitability. Authorities can change their issuing chain, and server file requirements vary. Run an external TLS check after installation to review names, dates and chain together. A public website should not require visitors to install an intermediate manually as a workaround for an incomplete server configuration.
Check proxies and multiple endpoints
When traffic passes through a CDN, the visitor-facing certificate may differ from the origin certificate. Review both relevant connections. With load balancing, verify every required deployment point rather than assuming the first successful response represents all servers. An intermittent old certificate can otherwise remain hidden until traffic reaches the forgotten endpoint.
Cloudflare’s Full strict guidance explains origin validation for that platform. Consult the equivalent official instructions elsewhere. If validation fails, correct the hostname, validity or chain rather than simply disabling checks. During a migration, also establish whether some traffic can still reach the old server and what certificate it presents.
Enable redirects after HTTPS works
Verify the secure destination before redirecting HTTP visitors to it. Preserve the appropriate path and required query parameters. An old product link should reach its corresponding product, not an unrelated home page. Record which layer owns the redirects so that the application, proxy and server do not apply conflicting rules.
Try HTTP and direct HTTPS entry addresses in a clean session and on mobile. Inspect response codes and the final destination with the technical team. Browser caching can conceal an old redirect. Additional policies such as HSTS should be planned after the underlying transition works, especially where subdomain coverage or long-lived browser behavior is involved.
Find mixed content
Images, scripts, stylesheets, fonts, embedded frames and API calls should use secure resources. The main page can have a valid certificate while HTTP requests inside it are blocked. Use Console and Network records to identify the exact request and the component that generates it. Include older content and campaign pages in the checks.
Changing an address from HTTP to HTTPS only works if the destination actually supports valid HTTPS. Unsupported external services may need replacement or removal. Clear relevant caches after correcting the real source and repeat the original interaction. Our mixed content guide explains the diagnostic sequence. Asking visitors to weaken browser protections is not a deployment fix.
Accept real user journeys
Submit a contact form, create a test account where relevant, and test login and logout. For a store, use the payment provider’s supported test environment for success, rejection and return flows. Confirm that the expected message or order reaches the appropriate system. A loaded image does not demonstrate that a form submission works.
Keep a compact record of the URL, action, expected result and observed result. Exclude passwords, card details and real customer information. If an error occurs, record the specific warning and affected request. Reproduce the original failing interaction after a fix; testing the desktop home page does not verify a fault that occurred only during mobile checkout.
Complete URL and maintenance checks
Internal links, canonical tags and sitemaps should agree on the secure URLs. Review crawling and redirect errors after launch using the HTTPS migration guide. Then record actual expiry, renewal automation and alert ownership. Installation acceptance should not leave the next renewal dependent on an unidentified person or an unmonitored mailbox.
If a critical action fails during the change, the technical team should follow the prepared rollback plan to a working secure configuration and investigate the cause. Do not treat HTTP fallback or disabled browser checks as routine acceptance. Explore our SSL options and web design service, or contact us with the affected hostnames and installation record for a coordinated review.